

05-04-2011, 11:05 AM

|
Thanks Anon.
|

05-04-2011, 09:18 PM
Jonathan Meer Wrote:Damn, it's cool to like Microsoft now? WHen'd that happen? Uh....Like since ever...Someone sounds Jelasaurus rex
[COLOR="DarkOrchid"]
The cure is a shotgun, the cure is whatever blunt instrument one can salvage.Whomever finds themselves too proper will be the first to perish. And you know nothing that matters now.[/COLOR]
05-04-2011, 09:44 PM
I actually don't like the xbox as much as the ps3. I think the hardware, as a whole, is far worse. Maybe do to coming out first, I dunno.
However, I do stand by windows over mac. Apple is a fucking abomination that won't die. 
05-04-2011, 10:55 PM
Psyren Wrote:Uh....Like since ever...Someone sounds Jelasaurus rex I don't really give a shit. I have Windows 7 and love it. I also use Google Chrome over IE9. And pro-Microsoft sentiment has hardly been a hallmark of the internet community en masse.  Mal Nova Wrote:I do apologize for using the word rape. There are four separate definitions for the word rape, two of which describe vegetation... 
05-04-2011, 11:07 PM
Jonathan Meer Wrote:I don't really give a shit. I have Windows 7 and love it. I also use Google Chrome over IE9. 7 is awesome. Just some bumps and quirks I dislike. Chrome is just less secure than IE9 otherwise it has more features I like. Searching in the address bar for example. To do that in IE in general I need to edit the registry to get it to do a google search. I have that file somewhere around here. That and I can highlight some text, right click, and press "search [insert highlighted text]" and search it. It's sexy. [SIGPIC][/SIGPIC]
  Fighting to the bitter end is an advantage when your opponent does not wish to perish.
05-04-2011, 11:09 PM
Yeah, I've heard IE9 is more secure. Chrome is just too fucking fast for me to switch, though.
Mal Nova Wrote:I do apologize for using the word rape. There are four separate definitions for the word rape, two of which describe vegetation...
05-04-2011, 11:10 PM
Jonathan Meer Wrote:Yeah, I've heard IE9 is more secure. Chrome is just too fucking fast for me to switch, though. Chrome works by loading only what it needs when it needs it. IE9 loads everything on the spot. [SIGPIC][/SIGPIC]
Fighting to the bitter end is an advantage when your opponent does not wish to perish.
05-04-2011, 11:56 PM
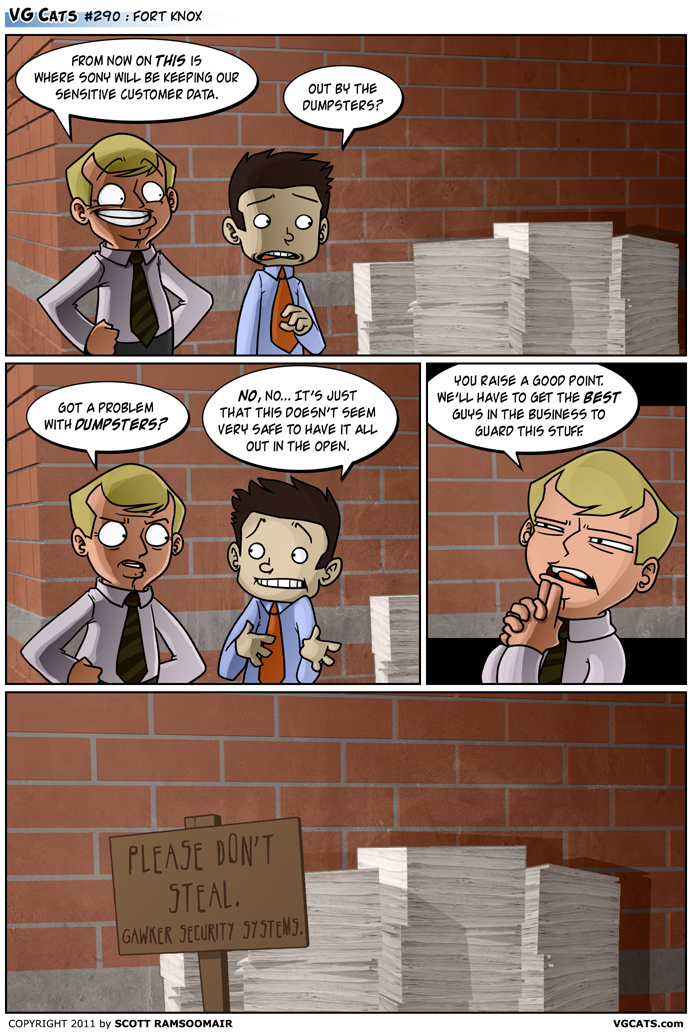
According to the company’s press release, “This information, which was discovered by engineers and security consultants reviewing SOE systems, showed that personal information from approximately 24.6 million SOE accounts may have been stolen, as well as certain information from an outdated database from 2007.”
While 12,700 card numbers may have been stolen, these were from non-U.S. cardholders, and they were taken from an outdated database. Furthermore, the card’s security codes were also not taken. While the hack is still worrisome, it’s nice to have some clarification on these issues. http://www.gameinformer.com/b/news/archi...-hack.aspx Edit: Japanese newspaper Nikkei.com claims that Sony fell victim to a second attack, a recent press release from Sony states that the recent credit card theft took place during the original attack on April 16. Unfortunately, Sony didn’t discover that its security had been compromised on this level until the morning of May 2. After discovering this additional information, Sony shut down its servers. Edit 2: "A Canadian law firm is proposing a class action suit that would have Sony pay for credit monitoring and fraud protection for two full years. It's been a challenging week for anyone working at Sony. The latest potential action being taken against the company emerges out of Canada, where Ontario resident Natasha Maksimovic is the representative plaintiff in a potential class action lawsuit demanding $1 billion for Canadian citizens who may be affected by the recent data breach. Toronto law firm McPhadden Samac Tuovi is filing the claim against Sony Japan, Sony USA, Sony Canada, and other Sony entities. Sony has 20 days to respond in its defense. In what might be one of the most inadvertently amusing lines in recent months, Maksimovic had the following to say in a press release yesterday: "If you can't trust a huge multinational corporation like Sony to protect your private information, who can you trust?" Who indeed?" http://www.gameinformer.com/b/news/archi...-sony.aspx Edit 3: Hackers that claim to have the stolen PSN data are attempting to sell credit card information on several message boards. They claim to have names, addresses, phone numbers, email addresses, birth dates, and full credit card information (number, expiration, and security code) for sale. TrendMicro security expert Kevin Stevens says that they offered to sell the information back to Sony, but the company refused. Stevens also says that 2.2 million credit cards are included in the database. Reports of fraudulent charges have been popping up on Twitter, on message boards, and in the inboxes of gaming journalists. There's no way to know for sure whether these claims are true, and even if they are there's no way to determine if they're tied to the PSN breach. This debacle has apparently gotten big enough for the government to take notice, as the Department of Homeland Security is now investigating the matter. "The Department of Homeland Security is aware of the recent cyber intrusion to Sony's PlayStation Network and Qriocity music service," says spokesman Chris Ortman. "DHS' U.S. Computer Emergency Readiness Team (CERT) is working with law enforcement, international partners and Sony to assess the situation http://www.gameinformer.com/b/news/archi...iracy.aspx 
05-05-2011, 12:03 AM
Poor Canada.

05-05-2011, 09:37 AM
Waffuru Wrote:Well, fuck non-US cardholders!That's a nice everything you have there. It would be a ssssssssshame if something happened to it. 
[SIGPIC][/SIGPIC]

05-05-2011, 07:59 PM
Damn Creepers.
A man in a wheelchair with a rocket launcher can make a big explosion once, then he's as weak as any other cripple.
-Some dude on the SWTor Forums
05-05-2011, 09:42 PM
Hacker group Anonymous is denying claims that members of the group breached PlayStation Network last month in an attempt to steal credit card and personal information of Sony's customers.
Sony said in its letter to the U.S. Congress yesterday that the company discovered a file planted by the intruders on one of its servers called "Anonymous" with the words "We are Legion" - the popular slogan used by the group. Responding to Sony's letter, Anonymous issued a statement today saying it has never engaged in credit card theft and that they are being framed by a group of "standard online thieves." The group previously stated it had no involvement with the PlayStation Network outage before Sony knew information was taken, saying "For once we didn't do it." Anonymous' statement can be read in full below: Last month, an unknown party managed to break into Sony's servers and acquired millions of customer records including credit card numbers. Insomuch as that this incident occurred in the midst of Anonymous' OpSony, by which participants engaged in several of our standard information war procedures against the corporation and its executives, Sony and other parties have come to blame Anonymous for the heist. Today, in a letter directed to members of Congress involved in an inquiry into the situation, Sony claimed to have discovered a file on its servers, presumably left by the thieves in question, entitled "Anonymous" and containing a fragment of our slogan, "We are Legion." In response, we would like to raise the following points: 1. Anonymous has never been known to have engaged in credit card theft. 2. Many of our corporate and governmental adversaries, on the other hand, have been known to have lied to the public about Anonymous and about their own activities. HBGary, for instance, was caught lying a number of times to the press, to the public, and to Anonymous itself (in this phone call, for instance, ( http://tinyurl.com/68pbdj8) CEO Aaron Barr makes a number of untrue statements regarding the intent of his "research," claiming for instance that he never tried to sell the information to the FBI when e-mails acquired soon showed that he had been set to do just that; executive Karen Burke was also caught lying to Bloomberg about having not seen an incriminating e-mail that she had in fact replied to just a few days before). The U.S. Chamber of Commerce lied about not having seen the criminal proposal created by them for Team Themis; Palantir lied about not having any idea what their employees were up to; Berico publicly denounced a plan that they had actively engaged in creating; etc. There is no corporation in existence will choose the truth when lies are more convenient. 3. To the contrary, Anonymous is an ironically transparent movement that allows reporters in to our operating channels to observe us at work and which has been extraordinarily candid with the press when commenting on our own activities, which is why reporters prefer to talk to us for truthful accounts of the situation rather than go to our degenerate enemies to be lied to. 4. Whoever broke into Sony's servers to steal the credit card info and left a document blaming Anonymous clearly wanted Anonymous to be blamed for the most significant digital theft in history. No one who is actually associated with our movement would do something that would prompt a massive law enforcement response. On the other hand, a group of standard online thieves would have every reason to frame Anonymous in order to put law enforcement off the track. The framing of others for crimes has been a common practice throughout history. 5. It should be remembered that several federal contractors such as HBGary and Palantir have been caught planning a variety of unethical and potentially criminal conspiracies by which to discredit the enemies of their clients. This is not a theory – this is a fact that has been reported at great length by dozens of journalists with major publications. Insomuch as that our enemies have either engaged in or planned to engage in false flag efforts, it should not be surprising that many of the journalists who have covered us, who know who we are and what motivates us – and who have alternatively seen the monstrous behavior of those large and "respectable" firms that are all too happy to throw aside common decency at the behest of such clients as Bank of America and the U.S. Chamber of Commerce – also have their suspicions that some capable party performed this operation as a means by which to do great damage to Anonymous in the public eye. Those who consider such a prospect to be somehow unlikely are advised to read about what was proposed by Team Themis in their efforts to destroy Wikileaks, and should otherwise take a few minutes to learn about COINTELPRO and other admitted practices by the U.S. intelligence community. The fact is that Anonymous has brought a great deal of discomfort to powerful entities such as Booz Allen Hamilton, Palantir, and much of the federal government; the Justice Department in particular is likely unhappy that our efforts revealed that it was they themselves who recommended the now-discredited "law firm" Hunton & Williams to Bank of America in order that the latter might better be able to fight back against Wikileaks. All of this is now public record, and anyone who finds it laughable that those or other entities may have again engaged in tactics that they are known to have engaged in in the past is not qualified to comment on the situation. Anonymous will continue its work in support of transparency and individual liberty; our adversaries will continue their work in support of secrecy and control. The FBI will continue to investigate us for crimes of civil disobediance while continuing to ignore the crimes planned by major corporations with which they are in league. We do not forget, even if others fail to remember. We not forgive, even if others forgive our enemies for those things for which we are attacked. We are legion, and will remain so no matter how many of our participants are raided by armed agents of a broken system. We are Anonymous. Dey sure got perty words erm herm. 
05-07-2011, 08:27 AM
That's pretty much what I thought when I heard about the news. This kind of thing isn't really anonymous's thing.
 Bra Wrote:People are dumb, essentially.
05-07-2011, 10:19 AM
I stopped thinking it wasn't anon's thing when you heard about them holding information regarding the employers families.
[SIGPIC][/SIGPIC]
|
|
« Next Oldest | Next Newest »
|


